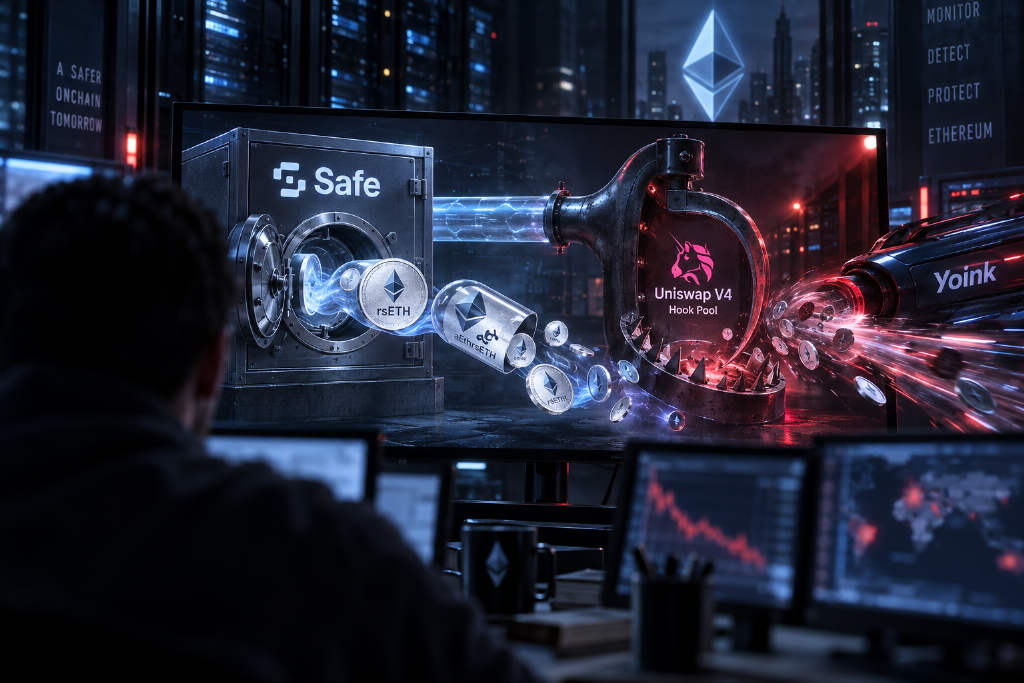
Ethereum2026-09-15 16:03:32MEV Bot Yoink Front-Runs $7.81 Million rsETH Exploit Targeting Safe Wallet on EthereumAn MEV bot known as Yoink front-ran a transaction tied to an rsETH exploit targeting a Safe wallet on Ethereum, in an incident PeckShield valued at roughly $7.81 million. Onchain data shows the Yoink transaction received 2,900 rsETH, sent 2,882.37 rsETH to the address 0xC70f00CD7E461686b04B0E912E309becA8b80ea0, and routed 17.63 rsETH to Uniswap v4’s Pool Manager. The pool then sent 18.95 ETH to the Yoink contract, which forwarded 18.93 ETH to the block builder. Both the Yoink transaction and the original attack transaction were included in Ethereum block 25980525 at 12:38 a.m. ET. Yoink landed in position zero, while the original attack reverted. Security researchers said that ordering matches a front-running pattern. BlockSec linked the exploit to a flawed authorization check in an executor contract tied to an enabled Safe module, while Blockaid said the attacker used a public keeper multicall to direct a custom Uniswap v4 liquidity module into an attacker-created hooked pool, where aEthrsETH was unwrapped into rsETH.870
Kelp2026-09-15 06:11:44Kelp Freezes rsETH Transfers for One Address for 24 Hours, Says Token Remains Fully BackedEthereum restaking protocol Kelp said on Sept. 15 that it detected suspicious activity involving an address that received rsETH several hours earlier and has placed a temporary 24-hour pause on that address. During the restriction window, rsETH cannot be transferred into or out of the address. Kelp said its contracts remain secure and that rsETH is still fully collateralized. The protocol added that minting, withdrawals, and integrations are operating normally, and users do not need to take any action. The update followed an earlier alert from Blockaid, which said an unidentified user’s Safe wallet on Ethereum had been compromised. Confirmed losses currently stand at about $7.73 million in rsETH. The statement limits the action to a specific address rather than describing a protocol-wide shutdown.540
Uniswap V42026-09-15 05:46:31Uniswap V4 Hook exploit drains about $7.73 million from a Safe walletA Safe wallet on Ethereum belonging to an unidentified user was exploited, with confirmed losses of about $7.73 million in rsETH, according to monitoring cited by BlockBeats from Blockaid. The attacker reportedly used a public Keeper Multicall to redirect a custom Uniswap V4 LP module in the Safe to a Hook Pool created by the attacker. From there, a malicious Hook was used to unwrap aEthrsETH into rsETH. The assets were then extracted by Yoink MEV within the same block. The report did not identify the wallet owner and only described the loss as currently confirmed at around $7.73 million in rsETH.650
Gnosis2026-06-01 12:00:50Gnosis Pay Zodiac Delay Module Exploited, Gnosis Pledges Full User CompensationGnosis co-founder Martin Koppelmann confirmed the Zodiac delay module used by Gnosis Pay is being exploited, allowing unauthorized transactions from Safe wallets. Gnosis requested bridge validators to halt operations and will cover all user losses, ensuring full reimbursement, while retracting the emergency withdrawal notice.560